

Hack hits French blood agency facilities
Nov 05, 2026, 10:43 am


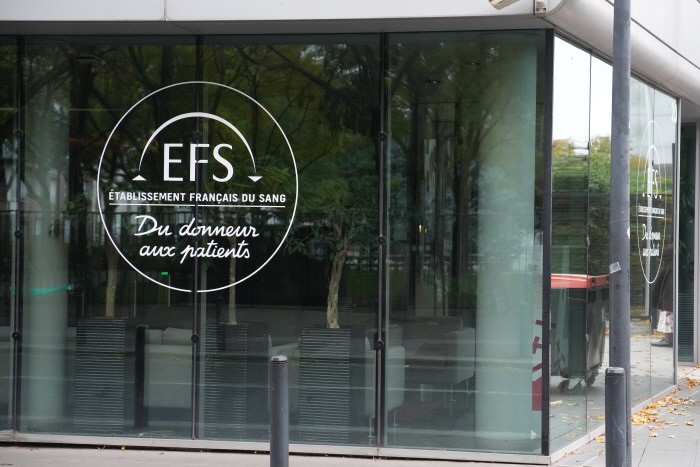 |
| The headquarters of the French Blood Establishment (EFS) in Saint-Denis, on the outskirts of Paris, France, on Nov. 4, 2026. /AP-Yonhap |
Amid a series of cyberattacks targeting commercial refrigeration facilities across Europe, a facility operated by a contractor for France's national blood service has also been confirmed as a target.
According to The Guardian, Euronews and other media outlets on Wednesday, the French Blood Establishment (EFS) said the control systems at three contractor-operated cold-storage facilities holding essential blood products were hacked on the night of Nov. 2.
French authorities said the attackers raised the temperature and defrost settings at the blood storage facilities to abnormally high levels. However, internal alarm systems were triggered, allowing technical staff to intervene before any blood products or samples were damaged.
EFS said it immediately transferred the affected supplies, including plasma bags intended for transfusions and pharmaceutical production, to alternative storage facilities. It also notified the French National Cybersecurity Agency (ANSSI) and the Health Ministry of the incident and strengthened its monitoring systems.
The incident is seen as part of a recent series of attacks targeting refrigeration equipment across European distribution networks. Over the past several days, refrigerator settings at supermarkets in more than 10 countries, including Belgium, the Netherlands, Italy, Germany and the United Kingdom, were raised to as high as 50 degrees Celsius, causing extensive property damage, including the disposal of spoiled food.
In France, remote refrigeration systems at approximately 700 supermarkets were hacked last month. Local financial institution Crédit Mutuel also reported being hit by a cyberattack.
The Guardian also reported that the U.S. Department of Defense was investigating the possibility of hacking in connection with refrigerator malfunctions at commissaries on several military bases early last month.
As the incidents spread, the European Union (EU) began seeking a coordinated response. EU spokesperson Thomas Regnier said the attacks were not isolated incidents and called for collective preparedness.
Security experts believe the attackers exploited inadequate vulnerability management, including insufficient security patching, even as the adoption of Internet of Things (IoT) technology has expanded remote control of refrigeration systems.
Various possibilities have been raised regarding those responsible, ranging from a show of capabilities by a state-sponsored group to the actions of a lone hacker. However, neither the perpetrators nor their motives have been identified.
Some have also raised concerns about hybrid attacks by Russian state-backed groups following Russia's invasion of Ukraine in 2022. Western intelligence officials have pointed to Russia's involvement in various forms of sabotage across Europe.
Lee Jeong-eun
Most Read
-
1
U.S., Israel plan to resume strikes on Iran after..

-
2
Ukraine halts strikes on Russian oil refineries un..

-
3
China's fifth plenum to conclude amid expectations..

-
4
ASEAN to discuss Myanmar's return next month

-
5
AI-discovered PHP flaw triggers global cybersecuri..

-
6
Southeast Asian auto parts makers hit hard by Chin..

-
7
Trump envoy says U.S. no longer guarantees Middle..

PEOPLE


-
Address : In-Young Bldg., 34, Uisadang-daero 1-gil, Yeongdeungpo-gu, Seoul
Copyright by ASIATODAY CO., LTD. All rights resereved