

Coupang faces audit scrutiny over post-incident remedies
Sep 30, 2026, 09:39 am


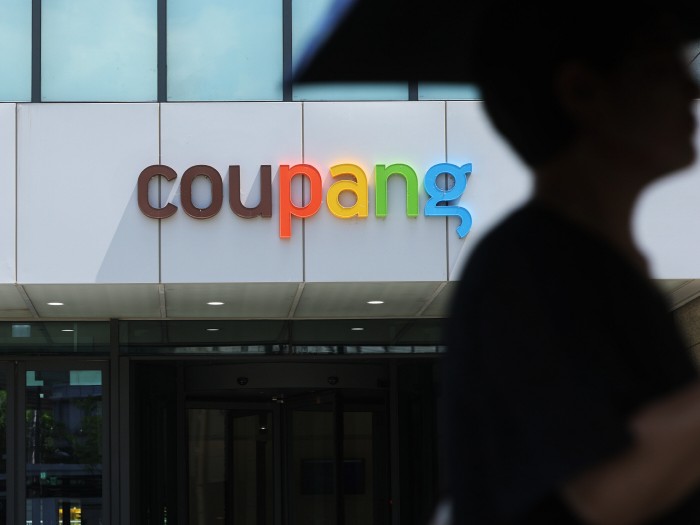 |
| Coupang headquarters / Yonhap News |
Coupang is expected to face scrutiny in next month's parliamentary audit over how much it has improved its security system following a personal data leak incident. Coupang's information security investment last year stood at approximately 134.9 billion won, up 51.6 percent from the previous year, but it failed to prevent the personal data leak. As the company launched an information security advisory committee composed of outside experts after the incident, the limits of its existing security system and the effectiveness of the recurrence prevention measures announced after the breach are likely to emerge as key points of contention during this year's audit.
According to industry sources on the 29th, the National Assembly's Science, ICT, Broadcasting and Communications Committee selected Coupang Chief Information Security Officer (CISO) Brett Matthes as a witness for the parliamentary audit, paving the way for an inspection of Coupang's security framework and post-incident improvements. If CISO Matthes appears as scheduled, he will take the witness stand before the National Assembly once again, following a hearing in December of last year.
First, a major point of interest is whether previous security investments have translated into genuine enhancements in security capabilities. According to the Korea Internet & Security Agency (KISA), Coupang's South Korean entity invested 134,936.72 million won in information security last year. This represents a 51.6 percent increase compared to the previous year. Compared with companies such as E-mart (8.1 billion won) and GS Retail (9.2 billion won), this investment figure is overwhelmingly high. Personnel dedicated to information security also expanded substantially. Last year, Coupang's dedicated information security workforce stood at 370.1 people, marking an increase of about 75 percent from the previous year (211.6 people).
It is also noteworthy that outsourced personnel accounted for a substantial portion of the workforce growth. While internal personnel increased by 42.1 from 162.7 to 204.8, outsourced staff climbed by 116.4 from 48.9 to 165.3. In effect, outsourced personnel made up about 73 percent of the total increase in dedicated staff. Consequently, the audit is expected to examine whether Coupang possesses sufficient internal capabilities for core controls, such as personal data access permissions and anomaly detection.
The effectiveness of the recurrence prevention measures introduced by Coupang after the breach is also subject to scrutiny. On the 15th, Coupang launched an Information Security Advisory Committee comprising seven outside experts. Heo Sung-wook, Chairman of the Korea CPO Forum, and CISO Matthes serve as co-chairs. Coupang plans to reflect the advisory findings in internal security policies and workflows to establish an industry-leading security system.
The crux lies in whether the advisory committee's recommendations are structurally designed to lead to tangible improvements in the security system. The audit is expected to examine what recommendations the committee has made so far, whether these recommendations are reported to Coupang's executive management and the Coupang Inc. board of directors, and whether the company is obligated to implement them. Whether the committee's recommendations and implementation outcomes will be disclosed to the public is another key observation point.
The issue of victim relief is also likely to be raised. Earlier, the Personal Information Protection Commission imposed a total fine of 624,681 million won on Coupang for legal violations, including personal data leaks and the unauthorized collection of user activity records. Of this sum, the fine concerning the personal data breach accounts for 423,575 million won. The Consumer Dispute Settlement Commission also recommended that the company pay 100,000 won in cash or Coupang Cash per person to applicants of a collective dispute mediation, but Coupang rejected the recommendation.
As Coupang responds to regulatory penalties and compensation demands through legal and procedural avenues while simultaneously pursuing its own recurrence prevention measures, the audit is anticipated to center on follow-up actions across both victim relief and security system enhancements.
Coupang maintains that it will incorporate the findings of the advisory committee into internal security policies and operational procedures. At its first meeting held this month, the company shared its ongoing customer data protection initiatives with committee members. An official from Coupang stated, "We will actively incorporate the experience and knowledge of experts to continue our efforts to enhance our security framework." The official added, "We will make efforts that go above and beyond global standards."
Choi Jeong-a
Most Read
-
1
Alteogen secures European patent for Keytruda SC,..

-
2
Trump shares map on social media labeling Strait o..

-
3
Celltrion seeks rheumatoid arthritis indication ex..

-
4
Trump demands rates fall below 1% as Fed hikes for..

-
5
Chinese e-commerce giants AliExpress, Temu and She..

-
6
China expels No. 2 military official Zhang Youxia..

-
7
Houthi rebels release video claiming downing of Sa..

PEOPLE


HEADLINE NEWS
- UNC says N. Korea violated armistice agreement in DMZ landmine explosion
- U.S. 30-year Treasury yield hits 5.613% intraday, highest since 2002 as bon..
- Netanyahu faces political crisis ahead of election over allegations he igno..
- Chinese Foreign Minister Wang Yi demands retraction of Takaichi's remarks o..
-
Address : In-Young Bldg., 34, Uisadang-daero 1-gil, Yeongdeungpo-gu, Seoul
Copyright by ASIATODAY CO., LTD. All rights resereved