

Major brokerages pour 55 billion won into information security
Oct 13, 2026, 09:54 am


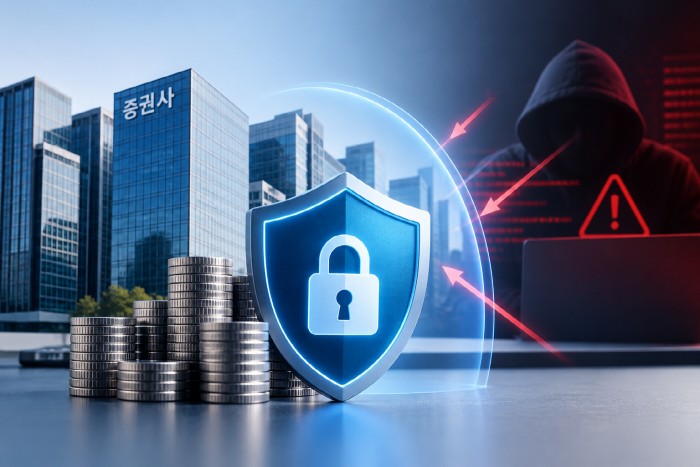 |
| This image was generated by AI. |
With a string of recent hacking incidents hitting financial institutions, public organizations, and universities, vigilance over cybersecurity is mounting. South Korea's securities industry was found to have prepared against cyber risks well before this turmoil erupted, investing over 55 billion won in information security. Across five major brokerage firms, total investments in information protection stood at roughly 55.2 billion won as of late June, with Korea Investment and Securities leading the pack at approximately 18.8 billion won.
Securities firms focused their investments on detecting and preemptively blocking signs of intrusion, prioritizing vulnerability assessments, behavioral anomaly detection, and perimeter access controls. With financial regulators recently ordering a comprehensive review of IT security systems, the industry's cybersecurity response is expected to tighten further.
According to the Korea Internet and Security Agency (KISA) on the 12th, among the securities firms that voluntarily disclosed their information security status as of late June, five detailed their primary investment categories: Korea Investment and Securities, Shinhan Securities, Hana Securities, SK Securities, and Daishin Securities. Among them, Korea Investment and Securities spent the most on information security at roughly 18.8 billion won, followed by Shinhan Securities with 17.1 billion won, Hana Securities with 10 billion won, Daishin Securities with 5.6 billion won, and SK Securities with 3.7 billion won.
Information security expenditure refers to funds allocated by companies to shield key data and systems from cyber threats such as hacking and personal data breaches, representing outlays drawn from total IT budgets specifically for security infrastructure and vulnerability management.
A review of the disclosed investments shows a clear focus on proactive defense, including anomaly detection, vulnerability management, and perimeter intrusion controls. Rather than settling for post-incident recovery, firms prioritized spotting early anomalies across internal networks and external endpoints while minimizing the likelihood of intrusion.
Korea Investment and Securities invested in an automated CVE (Common Vulnerabilities and Exposures) scanning and response framework, alongside upgrading its Endpoint Detection and Response (EDR) and Next-Generation Antivirus (NGAV) capabilities. This is seen as an effort to boost proactive defenses against emerging malware and breach indicators by automating known vulnerability checks and detecting abnormal activity across endpoint PCs and servers.
Shinhan Securities implemented new access control solutions for unstructured data and introduced an open-source vulnerability management platform. This move expands the firm's oversight to identify risks emerging from third-party open-source components while regulating access to and the exfiltration of internal files and images.
Hana Securities established a server antivirus system, broadened EDR deployment, introduced a firewall policy distribution system, and upgraded its information security portal. A Hana Securities official explained, "We enhanced anomaly detection and incident response efficiency by establishing a multilayered defense system running from individual endpoints such as employee PCs and servers through to centralized network monitoring," adding, "We also reinforced our surveillance framework by expanding server antivirus and EDR coverage."
Looking ahead, Hana Securities plans to bolster its defenses against AI-driven threats. The firm is working on deploying AI-powered web vulnerability scanners, an integrated vulnerability management system, and wireless backdoor detection mechanisms, while advancing its malicious app detection systems and API service security architectures.
SK Securities rolled out an enterprise-wide EDR solution and a supply-chain security management framework. The goal is to manage not only endpoint behavioral anomalies, but also exposure risks introduced through contractors, partners, and external third-party software.
An SK Securities official stated, "To tackle increasingly complex external attack vectors, we upgraded to proactive response solutions rather than basic detection systems," adding, "Moving forward, we will concentrate on refining architectures to efficiently intercept and spot novel attack methodologies."
Daishin Securities recently invested in overhauling its web security gateways, monitoring the dark web, and upgrading endpoint threat intelligence modules. The initiative aims to counter external risks while fortifying internal networks by blocking malicious sites and compromised file transfers alongside monitoring potential leaks of corporate data.
As cyberattack vectors against the financial sector grow increasingly varied, regulatory authorities have stepped in to inspect securities firms. The Financial Supervisory Service convened internal auditors from major brokerages, instructing them to re-evaluate their entire IT security infrastructure and review protocols. In response, brokerage houses are expected to further refine their security architectures, focusing on preemptive controls like vulnerability management and proactive threat detection.
Kwon Myung-joon, an analyst at Yuanta Securities, noted, "The spate of hacking incidents across the financial industry indicates that non-financial enterprises also face elevated hacking risks," adding, "As AI-driven hacking attacks gain momentum, attention toward cybersecurity is expected to climb substantially."
Park Ju-yeon
Most Read
-
1
Kia Sportage outperforms Mazda CX-5 in German auto..

-
2
Houthis launch successive attacks on Saudi airport..

-
3
Saudi Arabia, Iran hold first diplomatic talks to..

-
4
U.S. deploys carrier, 10,000 more troops to Middle..

-
5
Saudi airport in Riyadh struck again, leaving at l..

-
6
Putin's ally visits China on the 8th ahead of APEC..

-
7
Five ASEAN countries welcome Myanmar coup leader

PEOPLE


HEADLINE NEWS
-
Address : In-Young Bldg., 34, Uisadang-daero 1-gil, Yeongdeungpo-gu, Seoul
Copyright by ASIATODAY CO., LTD. All rights resereved